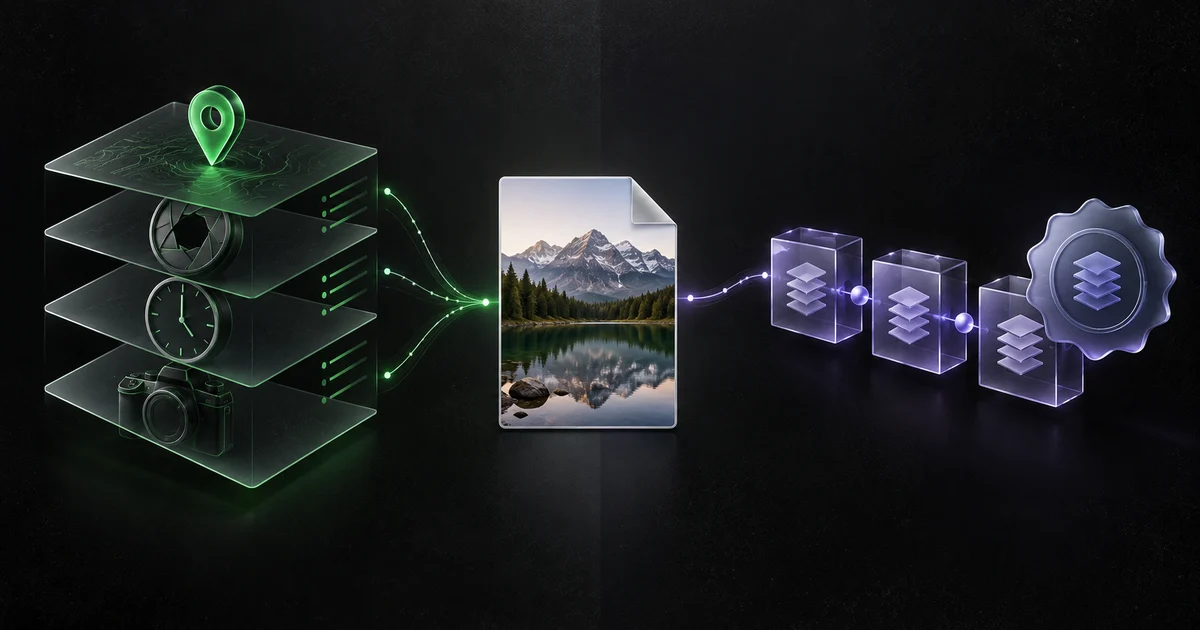
Two systems, two jobs
EXIF was designed for exchanging attributes associated with digital photography. Those tags are informative but not a chain of custody: ordinary software can remove, copy, or rewrite them.
The C2PA specification defines Content Credentials as a way to store or discover cryptographically verifiable provenance information. A manifest can describe actions, ingredients, metadata, and bindings to the asset.
| Question | EXIF | C2PA Content Credentials |
|---|---|---|
| Primary purpose | Record capture and image attributes | Record provenance and transformations |
| Common contents | GPS, date, camera, lens, exposure | Actions, ingredients, assertions, signatures |
| Tamper-evident | No | Designed to be, when validated |
| Can be copied or edited | Yes | Assertions are bound to a signed claim |
| Detection proves validity | Not applicable | No. Validation is a separate step |
Why marker detection is not verification
A file scanner can find byte patterns, containers, or references commonly associated with C2PA. That answers 'is there evidence of a payload?' It does not answer whether the claim signature is valid, whether the asset binding matches, whether the signer is trusted, or whether a remote manifest is available.
Cryptographic verification requires parsing the manifest, checking signatures and hashes, following the trust model, and reporting validation status. Products should clearly distinguish marker detection from that full validation process.
Privacy and authenticity can conflict
EXIF cleanup is usually about data minimization: remove location or device details before sharing. Content Credentials are usually about transparency: preserve a signed history so others can inspect provenance.
Removing a provenance payload may protect private workflow details, but it also removes information a recipient could use to assess origin. The right choice depends on whether privacy, attribution, or verifiable provenance matters more for that copy.
How NoTrace handles the distinction
NoTrace exposes supported EXIF and related metadata fields and can flag common embedded C2PA or Content Credentials markers. It can remove supported stale provenance payloads while cleaning or rewriting a copy.
NoTrace does not currently perform cryptographic C2PA manifest verification. That limitation is intentional and visible in the product and documentation.
See what your photo reveals.
The browser checker reads supported metadata locally. Your selected photo is not uploaded.
Frequently asked questions
Is C2PA just another EXIF tag?
No. Content Credentials use a manifest and cryptographic structures for provenance. They may carry metadata, but the trust and validation model is different from ordinary EXIF fields.
Does finding a C2PA marker prove an image is AI-generated?
No. A marker can indicate a related payload or container. You must validate and interpret the manifest to understand its claims, and the absence of credentials does not prove an image is authentic or human-made.
Sources and methodology
We prefer primary documentation and distinguish documented behavior from repeatable observation. Product limitations are stated directly.
- C2PA Technical Specification 2.4: Content CredentialsPrimary specification for manifests, assertions, signatures, and content bindings.
- CIPA: Exif 3.0 overviewOverview from the industry body responsible for Exif.
- Library of Congress: JPEG encoded file with EXIF metadataIndependent technical description of JPEG/EXIF structure and common attributes.